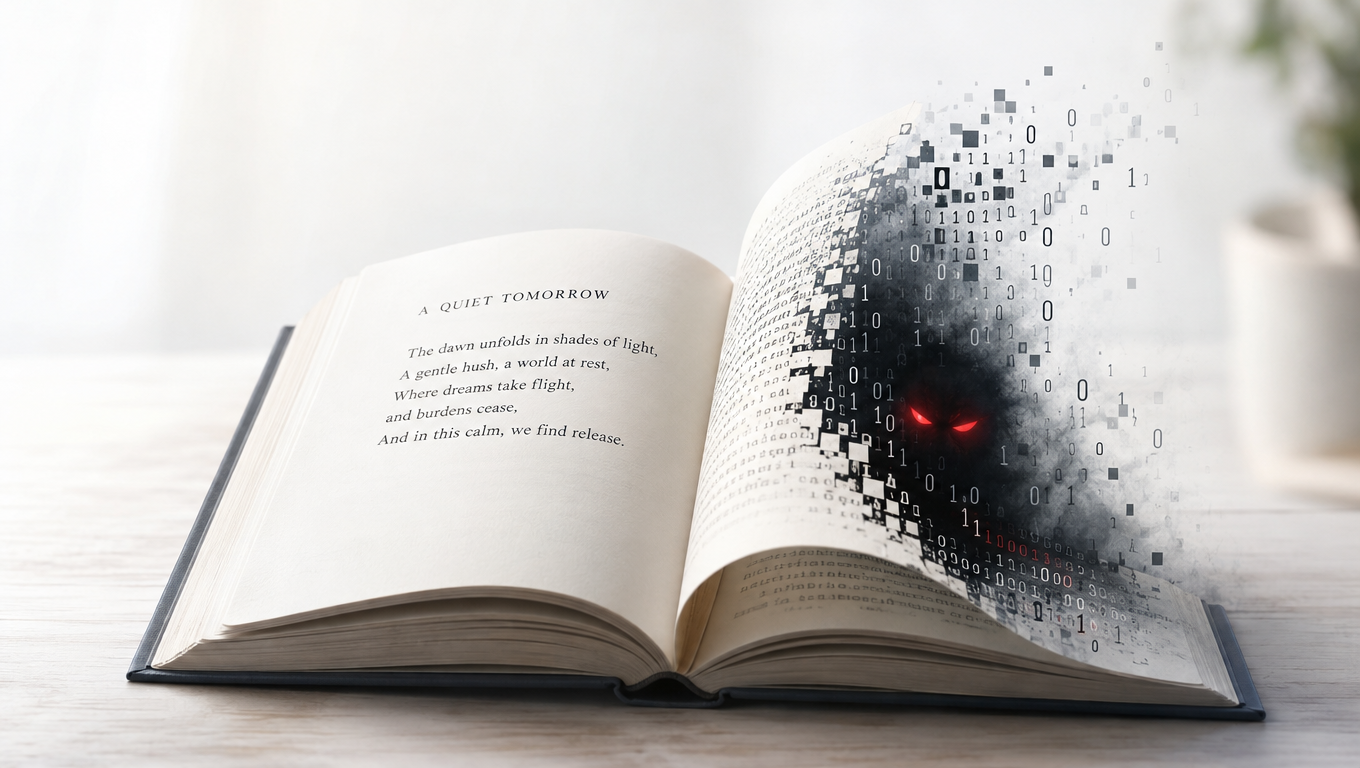
The Malware That Hides Inside a Poem. A hacker has managed to infect more than 3,000 servers worldwide with a highly unusual hacking tool: a poem.
Starting in April 2026, a piece of malware titled PoeLLM has been spreading across servers in the US and Western Europe. The attack harnesses a technique known as adversarial poetry, where harmful commands are concealed in what looks like creative writing. While this method has been known about for some time, this is the first time it’s been seen in the digital wild as a fully blown attack. In terms of capability, let’s just say it was breaching more than 800 servers a day at its peak.
Hidden in Plain Sight
The attacker, who is believed to be of Italian origin, posted a poem to a GitHub page. It was inside a file called “dash.css”, a rather uneventful name and unlikely to arouse suspicion. The poem itself was titled “On the Nature of Connection” and certainly sounds like something you would find in a poetry book. What made it a particularly interesting attack was that there were no suspicious links, no files to download, and no urgent call to actions. Just poetry. This simplicity was all part of the attacker’s plan.
Once the malware had been activated and infected a server, it quickly got to work. It would start by reading the poem and extracting specific words from certain lines. These words, once cross-referenced against a built-in dictionary, produced an IP address. This was used to redirect the infected PC back to the attacker’s control server. This allowed the attacker to create a botnet, one that they could easily redirect by just updating a few words in the poem.
In particular, PoeLLM targeted servers running AI tools such as Ollama and LiteLLM – both crucial for businesses running AI systems. Once these systems were breached, the malware used this hardware to mine cryptocurrency and infect other vulnerable machines. Clearly, the attacker wanted this attack to succeed for financial reasons, but the widespread digital chaos and headlines also make for an added bonus.
Three Things You Can Do to Protect Yourself
Your organization may not be running AI infrastructure, but this doesn’t mean your servers are immune. The methodology for this attack could easily be repurposed to compromise e-commerce, database, or even gaming servers. As long as it’s connected to the internet, your server could be at risk. Here’s what you can do to stay safe:
- Keep Your Software Updated: Many of the servers attacked contained vulnerabilities, making them easy pickings for the malware. Applying updates as soon as they’re available, therefore, is paramount for protecting your defenses.
- Don’t Expose Servers to the Internet: Where possible, you should limit the number of servers you make publicly accessible. If a service you use doesn’t need to be accessed from outside your network, keep it locked down.
- Monitor Any Unusual Activity: The PoeLLM attack recruited infected machines into botnets and mine cryptocurrency. Unexpected spikes in CPU usage can identify malicious activity, so it’s important that you keep an eye on performance. If anything looks out of the ordinary, dig a little deeper to discover the cause.
For more ways to secure and optimize your business technology, contact your local IT professionals.