by Ophtek, LLC | Jul 16, 2024 | future growth, hardware, IT infrastructure, maintenance, needs assessment, network infrastructure, Ophtek, performance, scalability, Software
In the digital age, it’s crucial for your business to have a robust IT infrastructure if you want to achieve long-term success and sustainability. An IT infrastructure, however, is a complex combination of services and components. Accordingly, building and...
by Ophtek, LLC | Sep 8, 2020 | Graphics Card, hardware, New PC, Ophtek, Processor, RAM
3 Things to Look at When Buying a New PC. The sheer range of PCs available makes choosing a new one very difficult. But in business there’s no time to waste, so you need to know what to look for. Take a look at the spec sheets for two different PCs in the same...
by Ophtek, LLC | Jun 5, 2018 | hardware, Repairs and Upgrades, Security, upgrade hardware
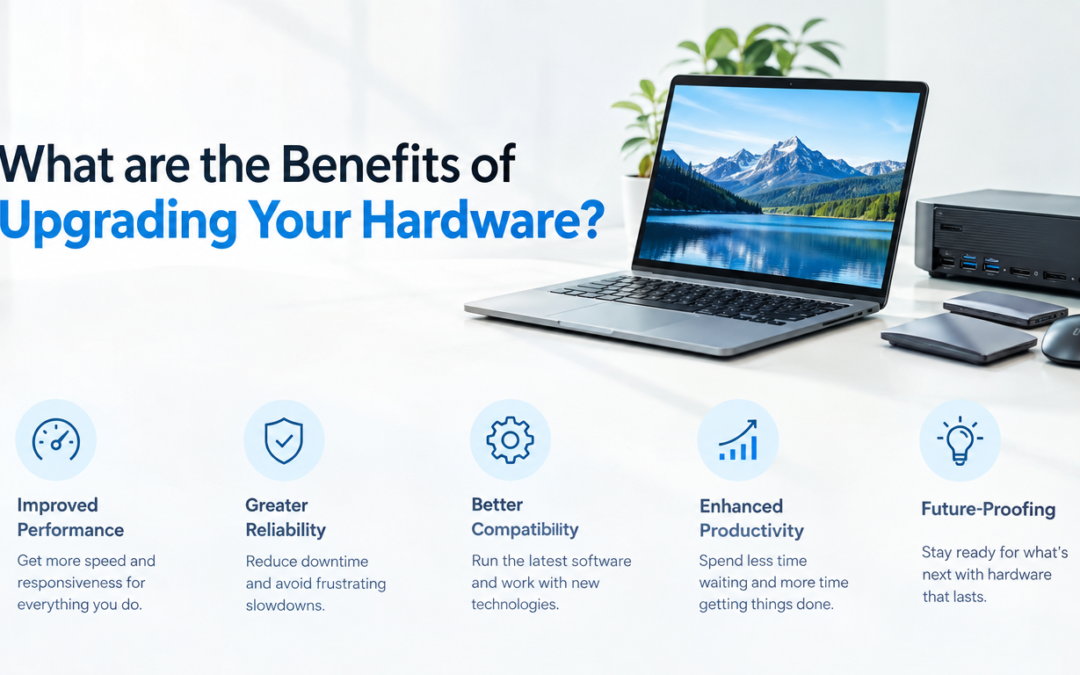
What are the Benefits of Upgrading Your Hardware? Upgrading hardware can be a costly affair, so it’s often easier to stick with your existing hardware. How many benefits, though, are you missing out on? New hardware is constantly being released, but there are...
by Ophtek, LLC | Jan 7, 2018 | Hacking, hardware
Nearly All PCs At Risk From Spectre and Meltdown Security Flaw. Microsoft has been forced into rushing out an emergency security update to help counter security flaws that have been discovered in modern processors. Discovered by Google’s Project Zero team,...
by Ophtek, LLC | Aug 29, 2017 | hardware, Office IT
Malware Upgrades to 64-Bit. Modern operating systems run on 64-bit systems, but they’re still capable of running 32-bit code and this is what hackers have always coded in. Until now. Guy Propper – security expert at Deep Instinct – has revealed that whilst...
by Ophtek, LLC | Aug 8, 2017 | hardware, Security
IBM Ships Malware Infected USB Drives by Mistake. Malware is a particularly virulent strain of hacking and can spread very quickly. However, when it gets help from a tech giant, it can spread even quicker. It’s now been discovered that IBM have, quite accidentally,...