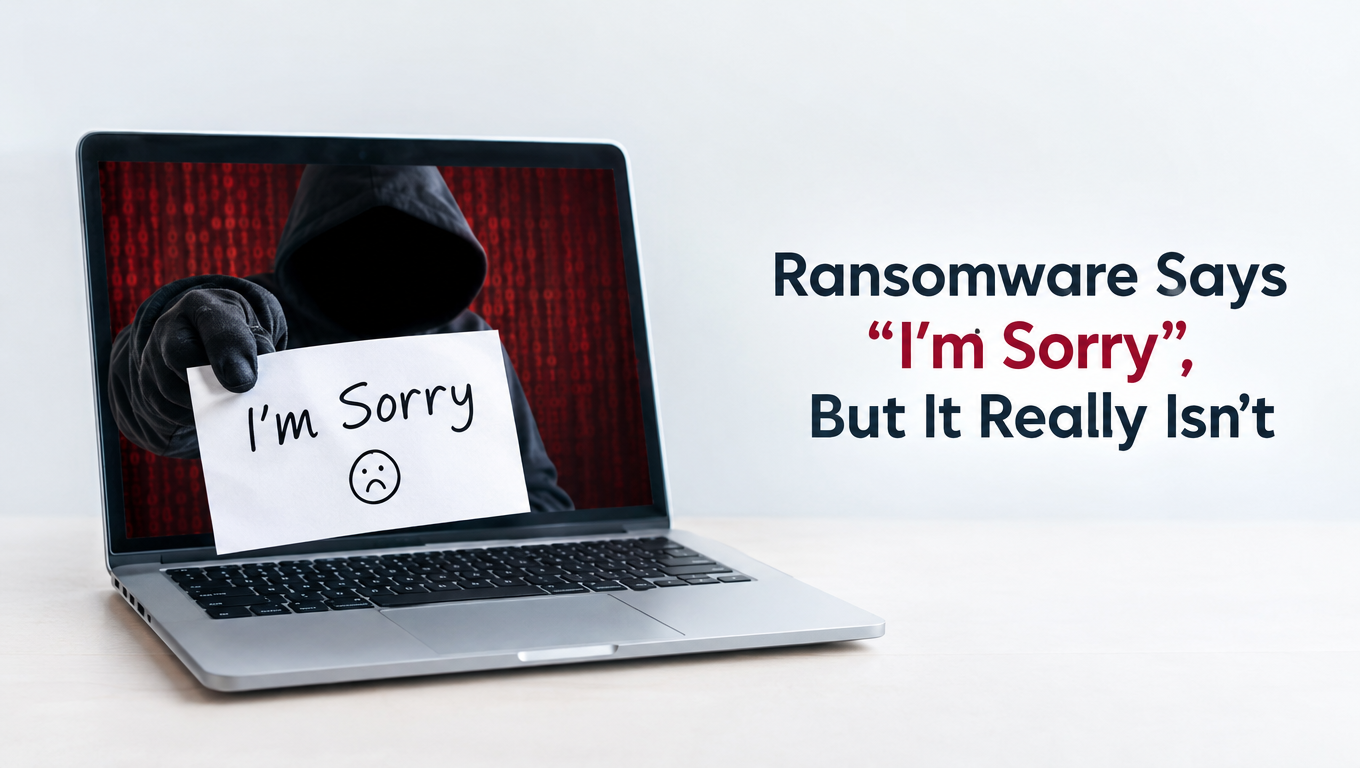
Ransomware Says “I’m Sorry”, But It Really Isn’t. Being hacked is always unpleasant, but a new strain of ransomware actually apologies for the inconvenience. However, it’s still a nasty piece of work.
Ransomware is a fairly aggressive form of malware in that it demands a ransom, so many PC users can find it particularly distressing. The I’m Sorry ransomware, though, decides to go against the grain, but only slightly. And, instead of just demanding the ransom (which I’m Sorry most certainly does), it prefaces this with a very polite notice which, unfortunately, fails to soften the blow.
As this is such an unusual approach to ransomware, I thought you would be interested in hearing a little more about it.
The exact location of the I’m Sorry source is rather unclear at the moment (which is what the authors of the ransomware will be aiming for), but it’s believed that it’s currently being distributed via third party downloads e.g. downloading files from torrents or free file hosting websites. These sources are very difficult to police due to the huge number of files available at any one time, so are perfect for obscuring the source.
As with all ransomware, the aim of I’m Sorry is to encrypt files and, in this particular instance, it encrypts files with a new file extension of I’m Sorry e.g. MonthlyReport.doc will be encrypted into MonthlyReport.imsorry and will not be accessible any more. However, if the user does want to access the file, I’m Sorry advises them to pay a ransom fee of $500 to obtain a key for decrypting the files back to normal.
What’s unique about I’m Sorry, though, is the manner in which it requests this payment as it advises the following: “Hello, I hate to inform you but your files have been encrypted. To get them back you must pay me a small fee”. This is certainly less aggressive than other strains of ransomware and I’m Sorry actually goes as far as providing details on how to set up a Bitcoin account for making the payment – such nice guys, right?
The fact remains, though, that no matter how polite and apologetic the hackers are – their ransom note signs off with “Once again, I’m sorry” – they’re still demanding a ransom, so their end goal is the same as all other ransomware hackers. And even if they have been kind enough to show good manners with their malicious software, they still find time to slip in a quick threat that the key will soon be deleted if the money isn’t paid.
Don’t Feel Sorry For Yourself
Thankfully, the threat level and sophistication of I’m Sorry is relatively low. And, reflecting its less than aggressive approach, it’s a fairly straightforward approach to remove I’m Sorry. Simply open your PC in Safe Mode and then run your antivirus software which should easily detect I’m Sorry.
Once this is removed you’re safe from any further files being encrypted, but you’ll still need to access your encrypted files somehow. Key to overcoming this obstacle is to ensure that your operating system has been set up to save System Restore points, this will allow you to restore your computer and all its files to a previous incarnation e.g. when they weren’t encrypted.
Although this isn’t the most difficult form of ransomware to remove, it still highlights the importance of never downloading files from unreliable sources. And it also hammers home just how crucial the System Restore option is, so you have to make sure that ‘restore points’ are regularly saved to return your PC to safer times if the need arises.
For more ways to secure and optimize your business technology, contact your local IT professionals.